A workspace per client
Each tenant gets its own subdomain, provisioned in one step — member sign-in, isolated transcripts, and scope pinned to that tenant’s zones.
A multi-tenant AI investigator for Cloudflare traffic and configuration. Each client gets a chat workspace; the agent queries their zones through a locked-down read-only choke point, verifies every finding, and writes an evidence-backed report.
A multi-tenant AI security investigator for Cloudflare: chat workspaces per client, read-only investigations through a locked-down egress choke point, adversarially verified findings, and evidence-backed reports — with changes only ever proposed, never applied without human approval. Live on our platform, onboarding by invitation: your workspace is provisioned with a read-only token you issue and can revoke. Write capabilities exist only as individually countersigned agreements — and every execution still requires a human click.
Machine-readable context: /ai-index.json
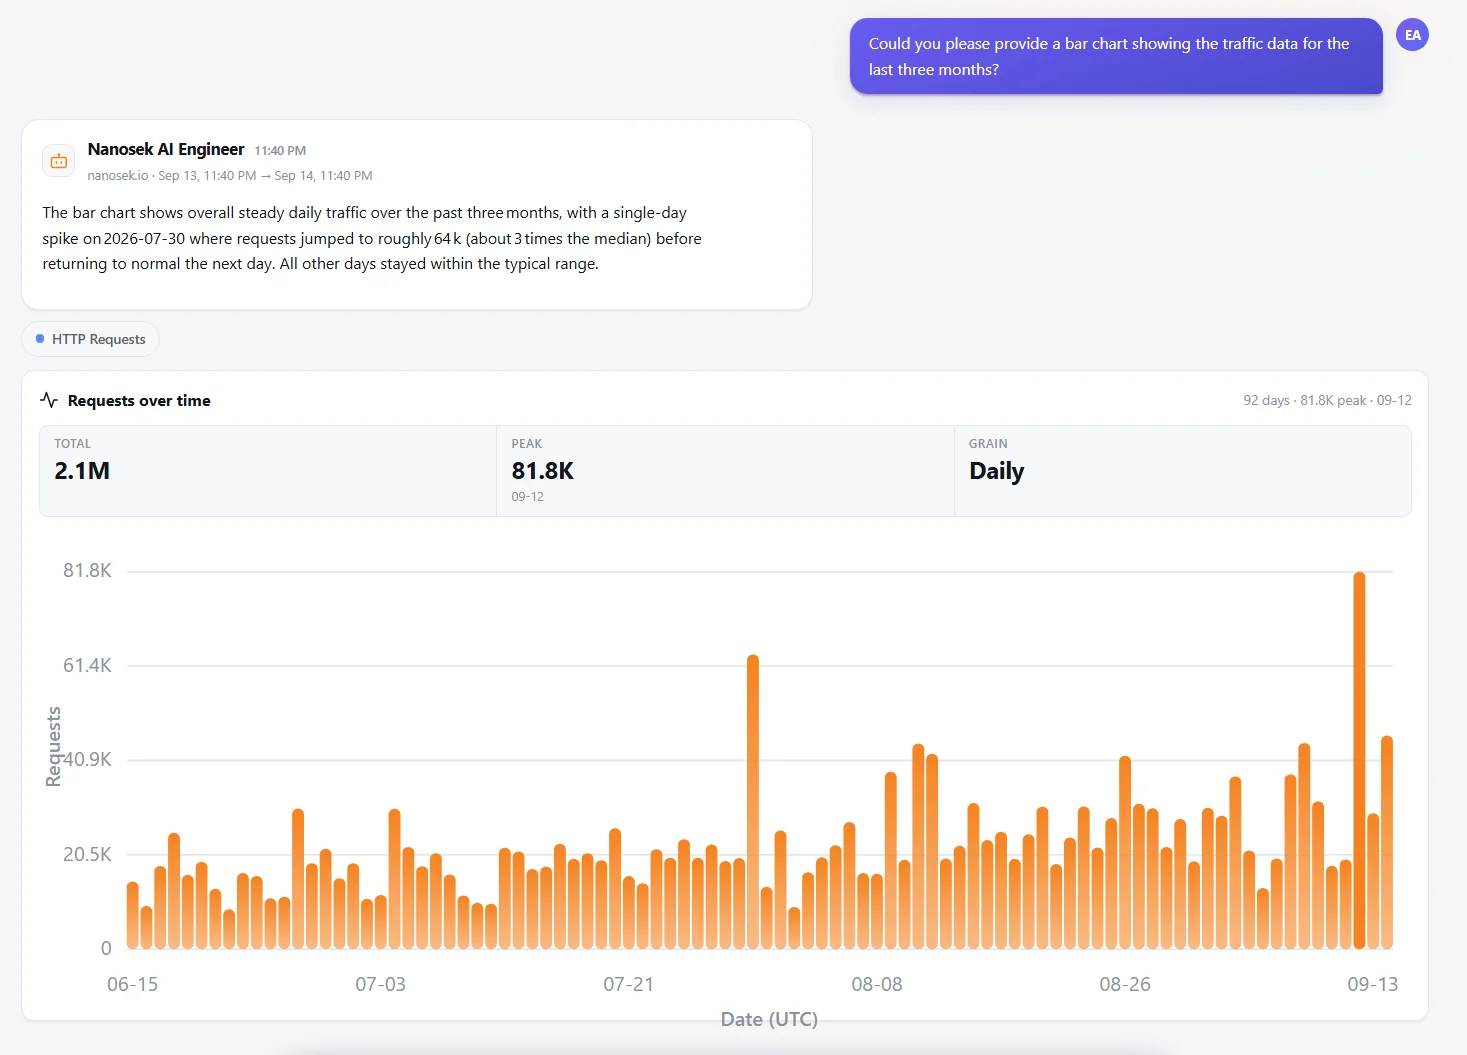
When traffic spikes or a rule misfires, someone opens five dashboards and starts guessing. The AI Engineer replaces that with a question: each client gets a chat workspace at their own subdomain, asks what happened, and the agent investigates — querying that tenant’s analytics, comparing windows, checking configuration, and citing everything it claims.
Deep questions launch a structured investigation: a scout pass frames the problem, parallel investigators pursue six angles, an adversarial verify pass tries to refute each finding, and the survivors are synthesized into a report with its evidence stored alongside it.
The security model is the product: the chat surface holds no write capability at all. Every Cloudflare call flows through one choke point that injects the tenant’s scope from our records — never from the chat or the model — enforces read-only access, and audits every call. If a customer wants the agent to propose changes, that specific capability is countersigned first, and even then a proposal only reaches Cloudflare after a human clicks approve.
Built on
Availability
Live on our platform, onboarding by invitation: your workspace is provisioned with a read-only token you issue and can revoke. Write capabilities exist only as individually countersigned agreements — and every execution still requires a human click.
How it works
The investigation pipeline
Findings must survive an attempt to refute them before they reach the report. Tap a stage.
Parallel investigators pursue independent angles using the seven analytics primitives — traffic concentration, window comparison, segment ratios, ASN composition, configuration snapshots, ruleset diffs and timelines. Every query runs through the read-only choke point and returns citable JSON.
Each tenant gets its own subdomain, provisioned in one step — member sign-in, isolated transcripts, and scope pinned to that tenant’s zones.
Scout → six parallel investigation angles → adversarial verification → synthesis. Findings that survive refutation become the report; the rest are discarded.
Concentration, window comparison, segment ratios, ASN composition, configuration snapshots, account-vs-zone ruleset diffs and traffic timelines — schema-validated, citable building blocks.
Reports are written to durable storage together with the raw evidence JSON behind each claim — auditable later, not just persuasive in the moment.
With a countersigned capability, the agent may propose a change as a card in the chat. It executes only when a member approves — through a separate executor that alone holds the write key.
A 585-test suite runs the real Worker against real migrations under production settings — session binding, tenant isolation, CSRF, header spoofing and the read-only gate are all asserted, not assumed.
The guarantees
GraphQL reads plus a GET-only REST allowlist. No other method, host or path can leave the choke point.
Zone and account filters come from our tenancy records only — never from the conversation, and never from the model.
Your read-only token is AES-256-GCM sealed and unsealed only for the duration of a single call, under a key the chat surface never holds.
Every API call — allowed, denied or failed — lands in the audit log.
Walkthroughs run on real data — yours. Tell us what you’re running and we’ll show you what Nanosek AI Engineer finds.
Whether you're migrating, hardening, or operating Cloudflare — Nanosek brings authorized MSP & ASDP delivery, rollback-ready cutovers, and managed operations after launch.